
Detect phishing emails with an interpretable Random Forest model that scores behavioral and linguistic features and explains every verdict to SOC analysts.
Cybersecurity Stack
Deep analysis and reviews of the weapons, platforms, and defensive tools used in professional offensive security.
Red Team Readiness Assessment
Red Team & Penetration Testing
A red team readiness assessment that tests whether you can safely run, detect and learn from full-scope adversary simulation mapped to MITRE ATT&CK.
A GitHub Actions security review that locks down secrets, token permissions, third-party actions, dependencies and deployment gates in your CI/CD pipeline.
SIEM Detection Engineering with Splunk/ELK
Security Analytics
SIEM detection engineering for Splunk and Elastic: build, tune and validate high-fidelity detections, threat hunts and dashboards in a 90-day program.
Vulnerability Management Operating Model
Vulnerability Management
A vulnerability management operating model that turns scan data into measurable remediation using asset context, exploitability data and repeatable workflows.
Web & API Penetration Testing Program
Application Security
A web and API penetration testing program combining manual exploitation, automated checks, CVSS-scored reporting and remediation guidance for developers.
Anatomy of an Enterprise Core Banking Penetration Test: The Consultant Mindset
Red Team & Penetration Testing
Inside a core banking penetration test: how an operator executes safely within tight rules of engagement and turns technical findings into C-level risk.
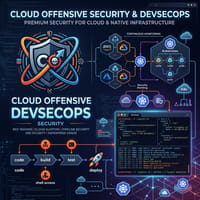
A multi-cloud red team story: from a GitLab pipeline to Kubernetes and chained AWS IAM roles, with the attacker logic and the DevSecOps fixes that stop it.
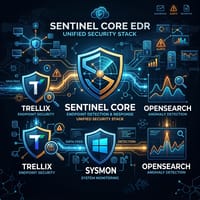
Modern EDR Stack: Trellix, Sysmon & OpenSearch
Endpoint Detection & Response
Build a hybrid EDR stack: Sysmon telemetry under Trellix Endpoint Security, fed into OpenSearch anomaly detection to catch fileless and LotL attacks.
Nmap as a Decision Engine: Operating Under Pressure During a Red Team Engagement
Red Team & Penetration Testing
Nmap as a decision engine in a time-boxed red team engagement: how an operator turns raw enumeration into real entry points when automated scanners fail.
Sponsored Links